
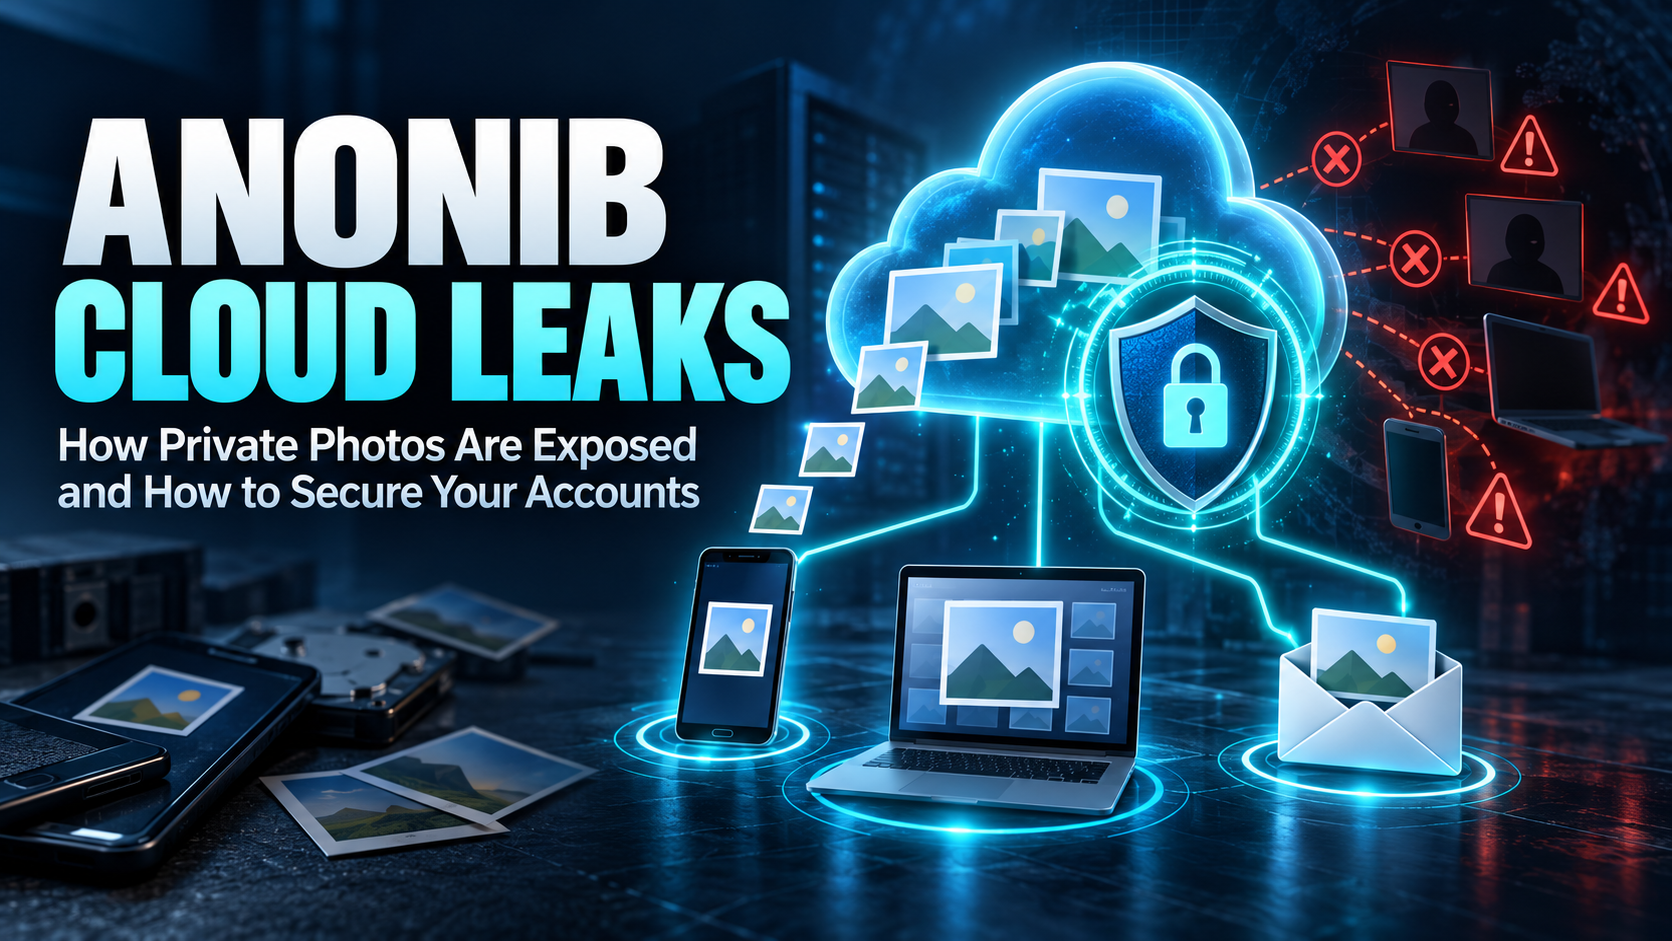
The history of AnonIB cloud leaks is a reminder that private photographs do not always reach abusive forums through a dramatic technical attack. Sometimes an offender steals a password. Sometimes they deceive someone with a fake login page. In other cases, an old device, shared album, recovery email, or former partner still has access that the account owner has forgotten about.
Dutch authorities seized the original AnonIB server in 2018 following an investigation involving stolen personal data and private photographs. Investigators said suspects had accessed victims’ email, social-media, and cloud accounts without permission. Contemporary reporting on the investigation describes how cloud-stored material became part of the case.
The original forum’s shutdown did not eliminate the wider risk. Stolen files can move through copycat boards, private groups, messaging services, and impersonation accounts.
If you are concerned that someone accessed your photographs, begin with your primary email account. It is usually the key that controls password resets and recovery access for everything else.
What Is an AnonIB Cloud Leak?
The phrase AnonIB cloud leak generally refers to private files taken from an online account and later posted on AnonIB or a similarly named imageboard without the subject’s permission.
The material may come from:
- Google Photos
- Apple iCloud Photos
- Google Drive
- OneDrive
- Dropbox
- Email attachments
- Shared albums
- Phone backups
- Social-media messages
- Old phones, tablets, or computers
Calling every incident a “cloud hack” can be misleading. The cloud provider itself may not have been breached. An offender may instead have entered the victim’s account using stolen credentials or retained access through a trusted device.
Whatever the technical route, responsibility belongs to the person who accessed or distributed the material—not to the person whose privacy was violated.
How Private Cloud Photos Can Be Exposed
Understanding the most common access points helps you close them without needing to become a cybersecurity expert.
Reused Passwords
When the same password is used across several services, the compromise of one account can put the others at risk. An attacker may try previously exposed email-and-password combinations on cloud-storage or social accounts.
Changing only the cloud password may not solve the problem if the primary email account still uses the same credentials.
Phishing Pages
A message may claim that someone posted your photograph, signed in to your account, or shared a document with you. The included link leads to a fake login screen designed to capture your password.
The message creates urgency because frightened people are more likely to act before checking the address.
Open the provider’s official application or type its address yourself instead of using an unexpected login link.
Access Through an Old Device
A forgotten phone, shared tablet, old laptop, or previously linked browser may remain signed in. Changing a password does not always end every existing session immediately.
Review the provider’s device list and manually remove equipment you no longer control.
Shared Albums and Links
A photograph can remain accessible through:
- A publicly shared album
- A partner-sharing feature
- A link that anyone can open
- A folder shared with an old email address
- A collaborative album containing unknown members
Someone does not necessarily need your password if a sharing link already grants access.
Compromised Recovery Information
An unauthorized recovery email address or phone number can let another person reset your password later. Removing suspicious devices is not enough when the recovery settings remain under someone else’s control.
Malicious Applications and Browser Extensions
Third-party applications may retain permission to read account information or access stored files. Browser extensions can also capture login details or change how pages behave.
Remove anything you do not recognize or no longer use.
Physical Access to an Unlocked Device
Someone who knows your phone passcode may be able to view photographs, approve login prompts, read verification codes, or change account settings.
Use a strong device passcode that is different from important account passwords.
Former Partners or Shared Accounts
A former partner may still know a password, belong to a shared album, have access to a family account, or possess a device that remains signed in.
This situation may involve technology-facilitated abuse, especially when digital access is combined with stalking, threats, location monitoring, or coercion.
Warning Signs That an Account May Be Compromised
One unusual notification does not always prove that someone entered your account, but several warning signs deserve immediate attention:
- A login notification from an unfamiliar device or location
- A verification code you did not request
- A password-reset email you did not initiate
- Unknown devices in your account settings
- Changes to your recovery email or telephone number
- Shared albums you did not create
- An unfamiliar partner-sharing account
- Deleted, moved, or downloaded files
- Messages sent from your account without your knowledge
- New email-forwarding rules
- Security alerts that suddenly stop arriving
- Applications with access that you do not recognize
- A password that no longer works
Apple lists unexpected authentication codes, unknown trusted devices, unexplained account changes, unfamiliar purchases, and a suddenly invalid password among the warning signs of a compromised Apple Account. Apple’s account-security guidance provides the current recovery steps.
Google similarly recommends reviewing recent security events, signed-in devices, recovery methods, connected applications, Gmail forwarding rules, Google Drive activity, and unexpected Google Photos sharing. Google’s compromised-account guide explains where to find these settings.
What to Do Immediately After Suspecting a Leak
Do not rush through random password changes. Work in an order that prevents the intruder from regaining access.
1. Use a Device You Trust
If you suspect that your phone or computer contains malware or monitoring software, use another trusted device to secure the account.
Update its browser and operating system before entering new credentials.
If a partner or household member may be monitoring you, consider whether sudden account changes could affect your physical safety. Use a trusted person’s device or contact a domestic-abuse support service when necessary.
2. Secure Your Primary Email Account
Your email account can usually reset passwords for cloud storage, social media, shopping services, and financial accounts.
Change the email password first. The new password should be:
- Unique to that account
- Long and difficult to guess
- Stored in a reputable password manager
- Unrelated to birthdays, names, or public profile information
Changing the email password before securing the email account itself can be ineffective if an attacker has added a forwarding rule or recovery address.
3. Review Recovery Methods
Check every:
- Recovery email address
- Recovery telephone number
- Trusted phone number
- Security key
- Authenticator application
- Passkey
- Backup code
- Account-recovery contact
Remove anything you do not recognize.
Regenerate backup codes if you believe someone may have seen or copied them.
4. Enable Multifactor Authentication
Multifactor authentication, also called two-factor authentication, adds another verification step beyond the password. This can prevent account access when a password is stolen.
CISA recommends enabling MFA because it makes an account more difficult to compromise with a password alone. CISA’s MFA guidance explains the protection.
When available, prefer:
- A passkey
- A physical security key
- An authenticator application
- A provider’s secure device prompt
- SMS verification
Text-message codes are still better than relying only on a password, but they can be affected by phone-account takeover or message forwarding.
Never approve a sign-in prompt you did not initiate.
5. Remove Unknown Devices and Sessions
Changing the password is important, but reviewing active access is equally important.
Remove:
- Phones you sold or gave away
- Old tablets
- Public or workplace computers
- Unknown browsers
- Unrecognized televisions or media devices
- Devices belonging to former partners
- Duplicate entries you cannot explain
Sign out everywhere if the provider offers that option, then sign back in only on devices you control.
6. Remove Suspicious Applications
Review connected apps and third-party permissions. Revoke access for anything you did not intentionally authorize.
Pay particular attention to:
- Photo-editing applications
- File-transfer services
- Backup tools
- Browser extensions
- Social-media schedulers
- Unknown email clients
- Applications installed outside an official store
Deleting an application from your phone may not revoke its account permission. Remove its access from the account’s security settings as well.
7. Inspect Email Forwarding and Filters
An intruder may create a rule that forwards security messages or hides password-reset emails.
Check:
- Automatic forwarding
- Mail delegation
- Inbox filters
- Blocked senders
- POP and IMAP access
- Automatic replies
- Deleted and sent folders
Remove unfamiliar rules and review whether account-security messages were deleted.
How to Secure Google Photos and Gmail
Open your Google Account directly and review Security & sign-in.
Review Recent Security Events
Look for password changes, new devices, altered recovery methods, and unfamiliar sign-ins. Mark activity you did not perform.
Check Every Signed-In Device
Open Your devices, select Manage all devices, and sign out anything you do not control.
A location can occasionally be approximate, so consider the device type, browser, and time as well as the map location.
Review Google Photos Sharing
Check:
- Shared albums
- Album members
- Partner Sharing
- Shared links
- Conversations containing photographs
Stop sharing anything that should no longer be available. If you used Partner Sharing, confirm that the listed account is correct.
Examine Google Drive Activity
Look for unexpected downloads, moves, deletions, or sharing changes. Review shared folders individually.
Check Gmail Settings
Remove unfamiliar forwarding addresses, filters, delegates, and third-party email access. A hidden forwarding rule can continue exposing new messages after the password changes.
Complete Google’s Security Checkup
Follow the provider’s recommended actions, update recovery information, and turn on 2-Step Verification or a passkey.
Do not access the security page through an email claiming your photographs were leaked. Open Google’s application or account page independently.
How to Secure iCloud Photos and Your Apple Account
Apple recommends changing the Apple Account password, reviewing personal and security information, removing unknown devices, and confirming control of every connected email address and phone number.
Review the Apple Device List
On an iPhone or iPad:
- Open Settings.
- Select your name.
- Scroll through the device list.
- Select any device you do not recognize.
- Remove it from the account.
You can also review devices through Apple’s official account website.
Check iCloud Photos and Shared Albums
Review Shared Albums, Shared Library membership, and any sharing links you previously created. Remove unknown participants and stop sharing links that are no longer needed.
Change the Device Passcode
If another person knows your iPhone passcode, changing only the Apple Account password may leave the device vulnerable.
Choose a new passcode that is not based on an address, birthday, or repeated pattern.
Turn On Two-Factor Authentication
Two-factor authentication helps prevent someone from signing in with only a stolen password. Review trusted phone numbers at the same time.
Consider Stolen Device Protection
Apple recommends Stolen Device Protection for added security when someone obtains an iPhone and knows its passcode. Availability and behavior depend on the device and software version.
Use Safety Check When Personal Sharing Is a Concern
On an iPhone with iOS 16 or later, Safety Check can review people, applications, connected devices, privacy permissions, and account access. It also provides an Emergency Reset option to stop sharing quickly.
Open:
Settings → Privacy & Security → Safety Check
Apple advises users to consider personal-safety consequences before making changes, particularly when another person may react to losing access. Apple’s Safety Check guide explains the available options.
How to Secure OneDrive and a Microsoft Account
If private files are stored in OneDrive, review your Microsoft account separately.
Start by checking the Recent activity page. Microsoft says significant events may include login attempts and profile changes. If you find activity you did not perform, choose Secure your account and follow the recovery process. Microsoft’s recent-activity guide explains what appears there.
Then:
- Scan the device for malware.
- Change or reset the Microsoft password.
- Review recovery information.
- Turn on two-step verification or passwordless sign-in.
- Remove unfamiliar devices.
- Review OneDrive sharing links.
- Check Outlook forwarding and automatic replies.
- Remove unknown connected applications.
Microsoft advises scanning a potentially infected computer before changing the password so malicious software cannot immediately capture the new credentials. Its compromised-account guide covers the recovery order.
Review Old Devices and Local Backups
Not every leak comes directly from current cloud access. Private files may still exist on:
- Retired phones
- Old laptop drives
- Memory cards
- External hard drives
- Automatic computer backups
- Messaging-app folders
- A former partner’s device
- A repaired or resold device
Before selling or giving away a device, sign out of accounts, remove it from trusted-device lists, and perform the manufacturer’s full erase procedure.
Deleting a photograph from the phone’s gallery may not delete it from cloud storage, a shared album, a synced computer, or the recently deleted folder. Review each location separately.
Protect Your Mobile Number
Your telephone number may receive recovery links and verification codes. Contact your mobile carrier and add an account PIN or other protection where available.
Ask whether:
- Unauthorized forwarding is active
- An unexpected SIM or eSIM was added
- Recent account changes occurred
- Another person is authorized to manage the plan
- Stronger port-out protection is available
A shared family plan may allow its manager to see certain account details. Understand who controls the plan before relying on the number as your only recovery method.
If the Images Have Already Been Published
Account security stops further access, but it does not remove files already posted.
Take these additional steps:
- Preserve the page URL and limited contextual evidence.
- Report the content to the hosting platform.
- Request removal from Google and Bing.
- Use StopNCII.org if you were an adult when the image was created and still possess the file.
- Use Take It Down if you were under 18 when it was created.
- Report threats, stalking, or extortion to an appropriate support or law-enforcement service.
- Do not pay someone who promises to stop sharing the files.
Link internally to your related guide: AnonIB Search Results: How to Remove Images and Personal Information.
If someone threatens to publish more material unless you send money or additional images, treat it as sextortion. Do not comply with the demands, preserve the messages, block the account after saving evidence, and seek specialist help.
Privacy Settings Cannot Transfer Responsibility to the Victim
Security guidance is useful, but it must not become victim-blaming.
A person is allowed to create, save, or privately share a photograph. That does not give another person permission to steal or publish it. Strong passwords reduce risk; they do not excuse hacking, coercion, or non-consensual image sharing.
The wrongdoing remains the uploader’s responsibility.
Does Deleting a Cloud Photo Remove Every Copy?
No. The file may remain in a recently deleted folder, shared album, synced device, local backup, message attachment, or another person’s account. Review each service and connected device separately.
Can Someone Access My Photos After I Change My Password?
Possibly, particularly if an existing session remains active, an app still has permission, or the attacker controls a recovery method. Sign out unknown sessions and review devices, applications, and recovery settings.
Is Two-Factor Authentication Enough to Protect Cloud Photos?
It greatly improves security, but it is not the only step. You must also protect the device passcode, recovery email, trusted phone numbers, shared albums, and connected applications.
Should I Delete My Entire Cloud Account?
Usually, securing the account and correcting its sharing settings is more practical than immediately deleting it. Deletion can also remove evidence or important files. Download essential non-harmful data safely and consider professional guidance before making an irreversible decision.
Build a Smaller Exposure Surface
Good account security is less about one perfect setting and more about removing forgotten access.
Use unique passwords, enable strong authentication, review devices every few months, close old sharing links, remove unused applications, and keep recovery information current. Begin with email, then secure cloud photos, social accounts, devices, and your mobile number.
If you already found private material online, work on removal and account security at the same time. Removing one post addresses the visible harm; securing the account helps prevent more files from being taken.

2 Comments
Pingback: AnonIB and Doxxing: How Personal Information Gets Exposed - anonib
Pingback: AnonIB Search Results: How to Remove Images and Personal Information - anonib